You focus on your business. We handle risk and compliance.
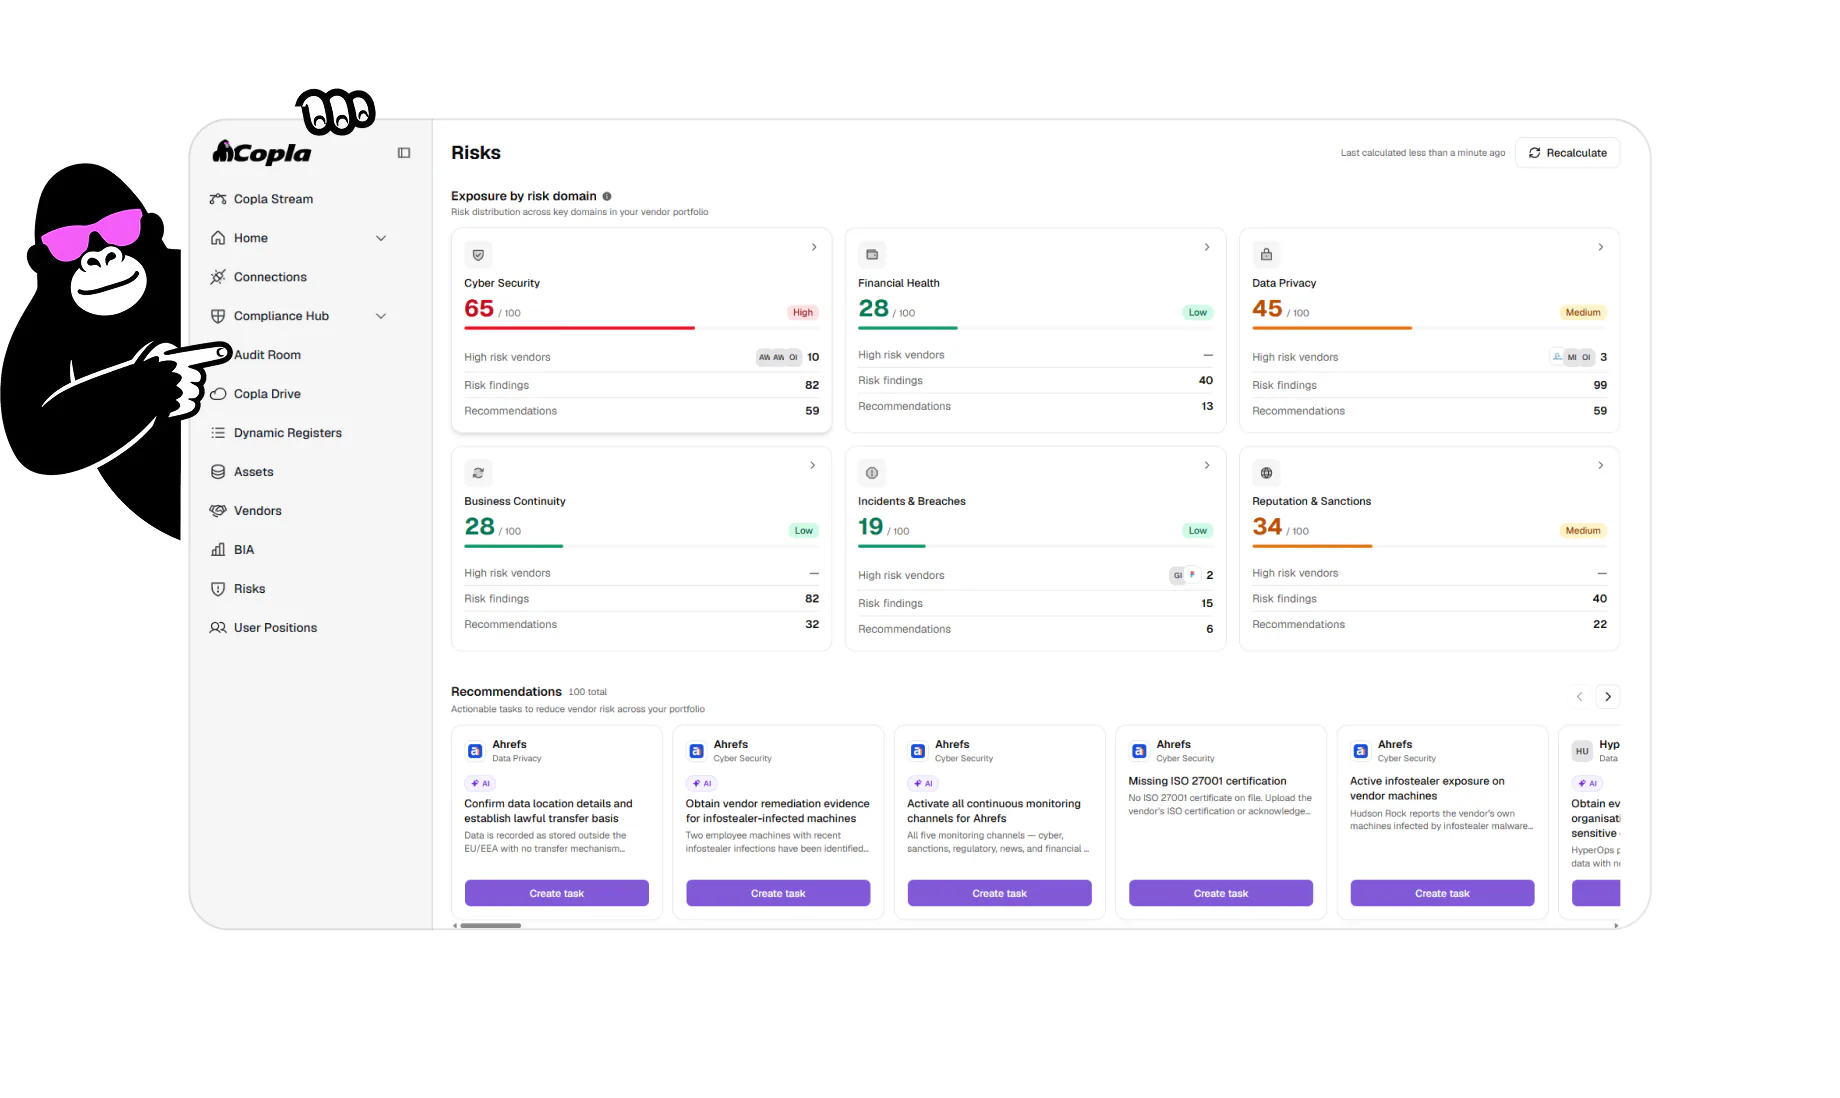
Copla combines automation, AI and hands-on CISO guidance so you can manage compliance, risk and vendors in one system — audit-ready and operationally resilient across frameworks, standards and regulations such as DORA, NIS2, ISO 27001, SOC 2 and more, well past the day you certify.
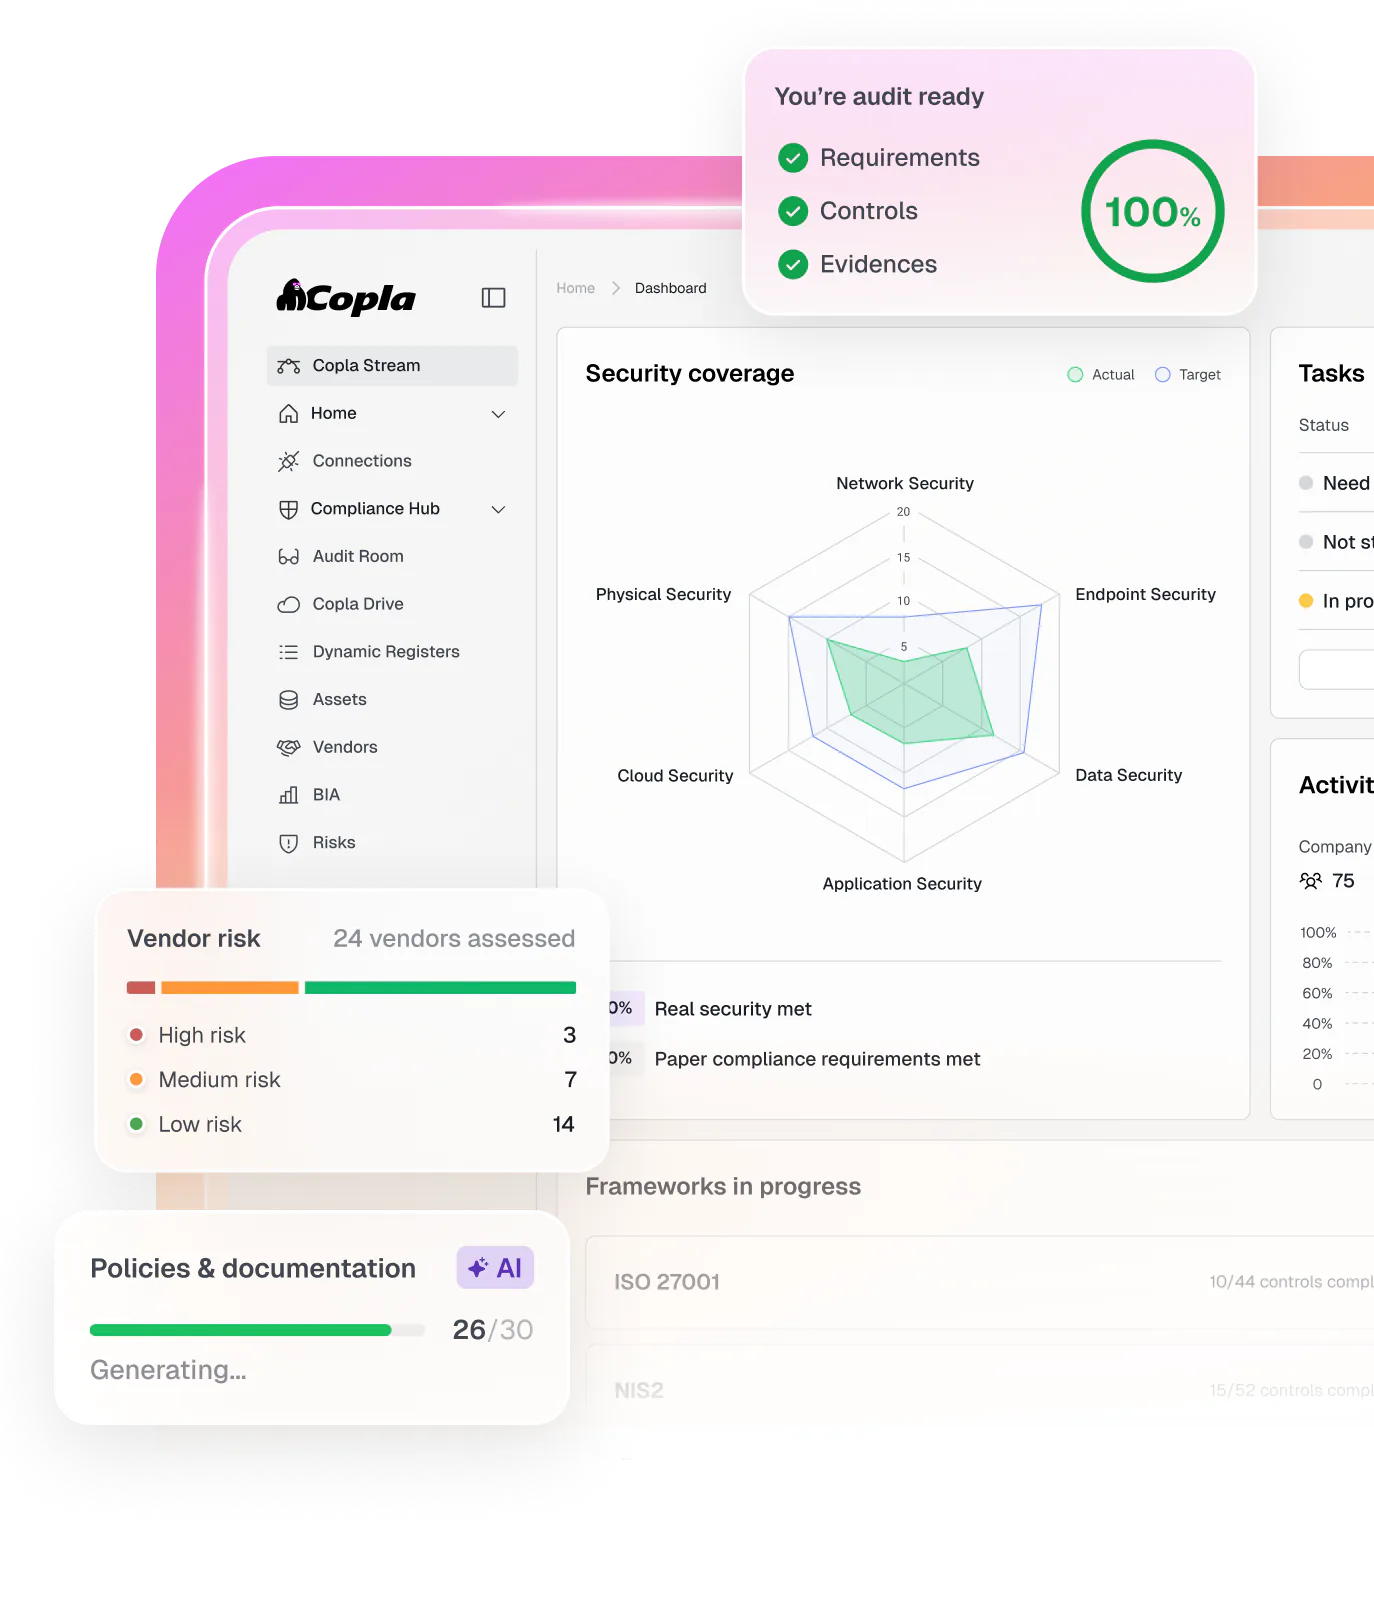
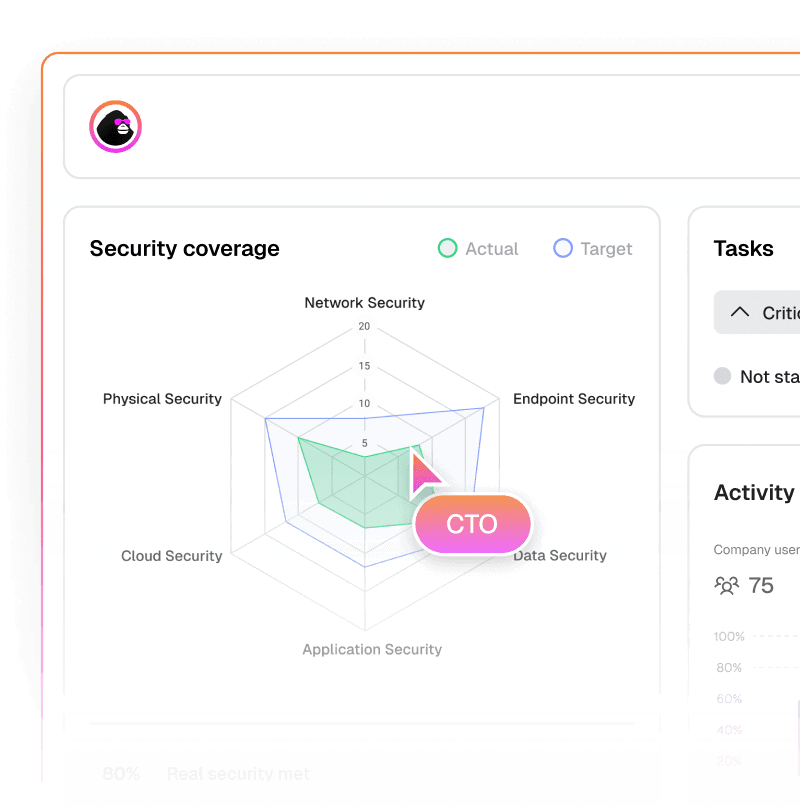
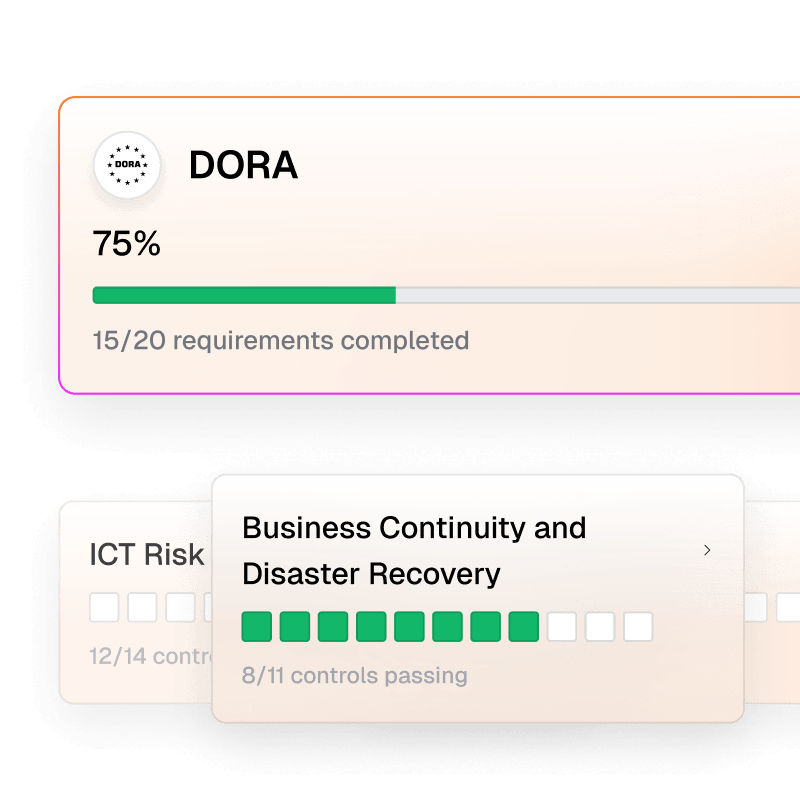
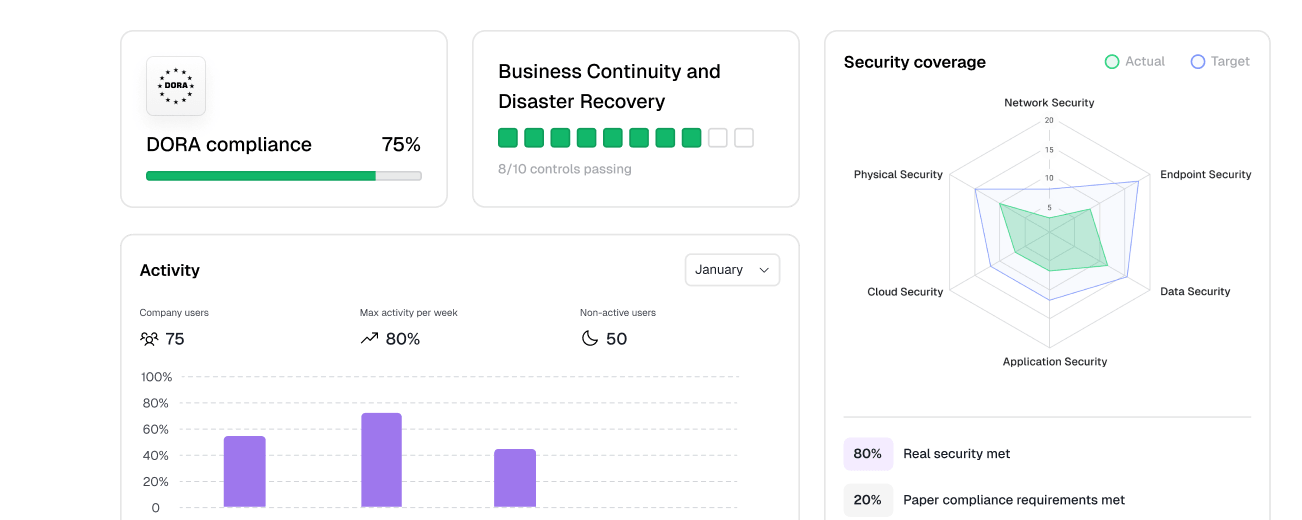
One system of record for compliance, risk and vendors — every register, control and document lives in the same place, you can always see where evidence and ownership stand.
Maps your risks to the controls and requirements that actually apply, then turns everyday work into evidence — reviewed by an in-house CISO before an auditor sees it.
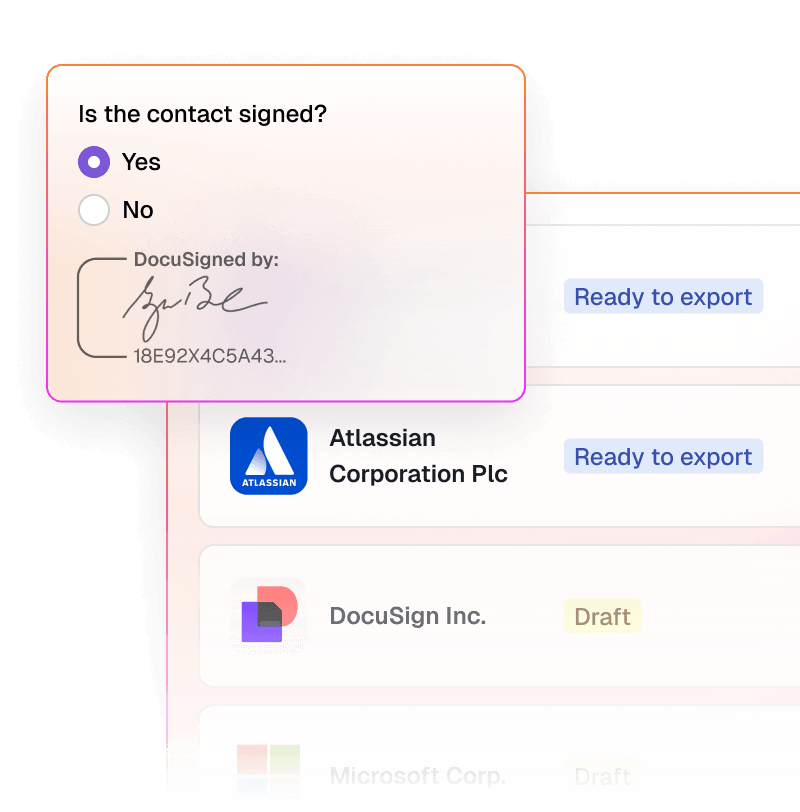
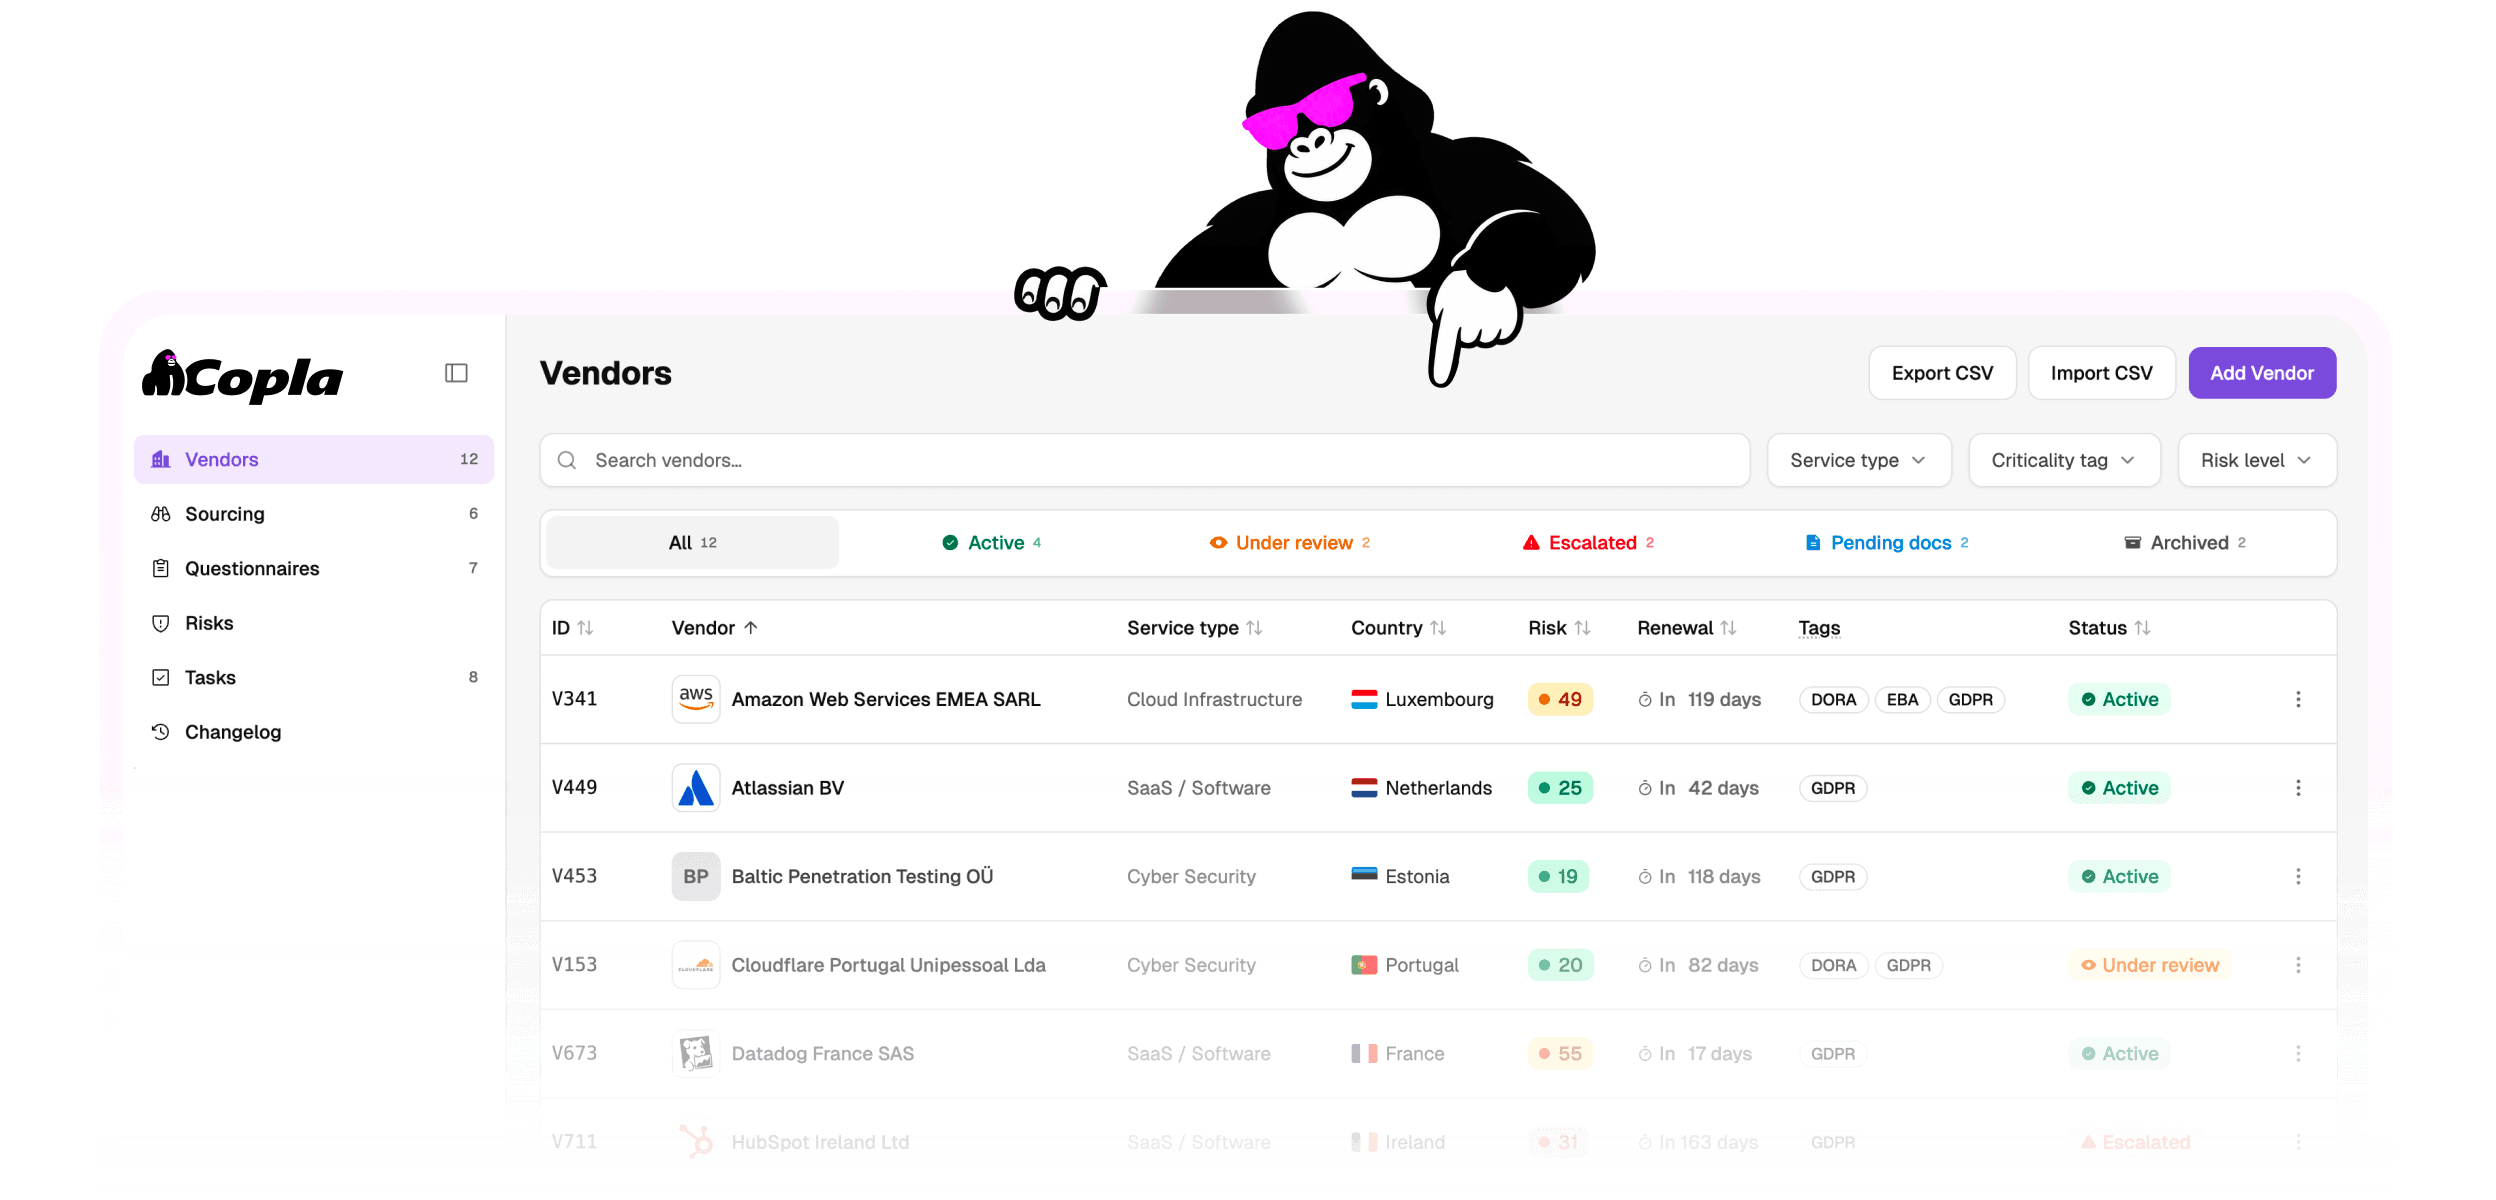
Keeps your DORA Register of Information structured, validated and traceable as providers, contracts and classifications change through the year — export-ready, not spreadsheet-rebuilt.
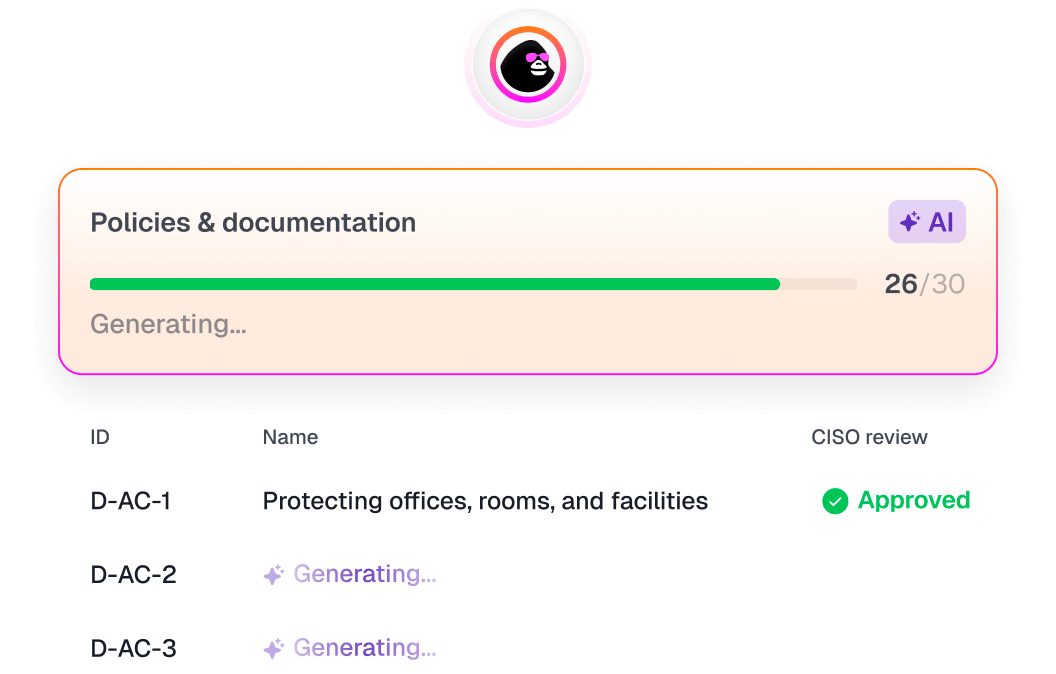
Generates and maintains policies from your actual operations, not a template pack, linked directly to the controls and risks they support and updated as things change.
Builds the system that runs your information security day to day — risks, policies, controls and evidence in one structured programme that stays live between audits.
A dedicated CISO team reviews your evidence, sits in on audits and interprets what each framework actually requires for your business, without the overhead of a full-time hire.
Hands-on evidence review, not a chatbot
Specialists across DORA, ISO 27001, NIS2 and SOC 2
Compliance can feel overwhelming when you’re not sure what needs to happen first.
Documentation takes too much time
Policies and compliance documents take hours to create and even more time to keep updated.
Third-party risk is hard to manage
Vendor assessments, contracts and renewals quickly become scattered and difficult to track.
Audits are harder than they need to be
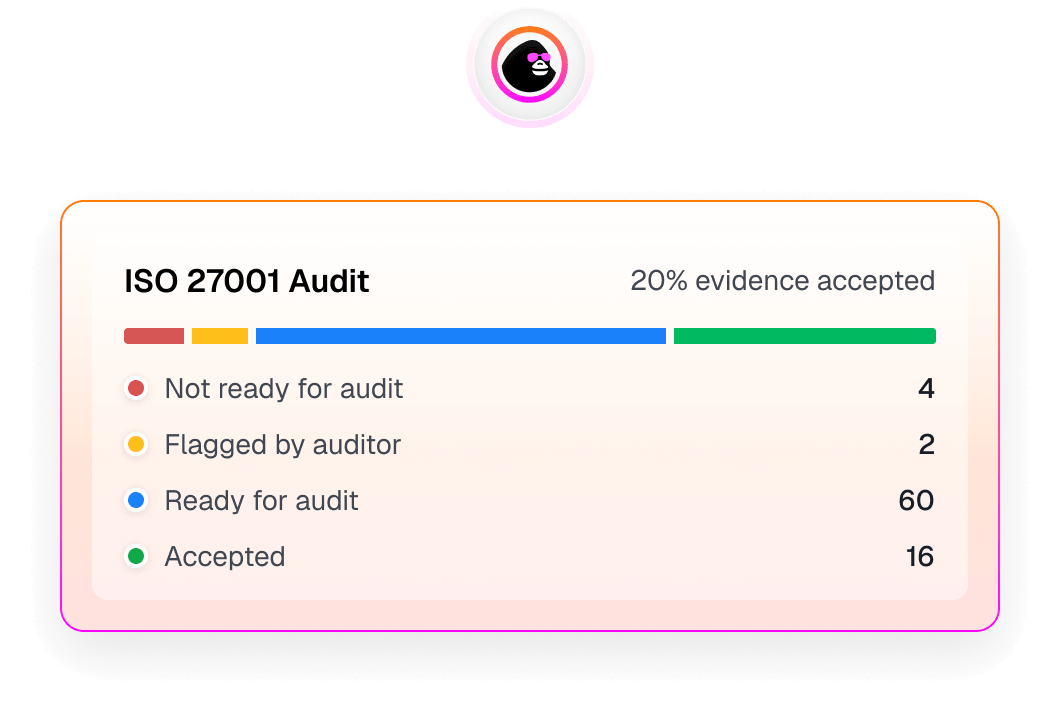
Auditors need a clear, structured view of your controls, evidence and ownership.
Start with a few simple inputs. Copla maps what you need to do, prioritises the work and guides you through it.
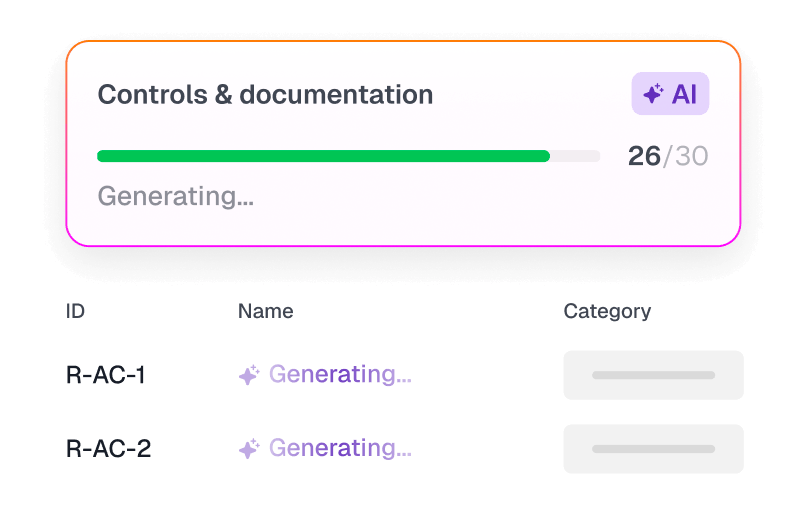
Generate and maintain the documentation you need with AI, with CISO review where it matters.
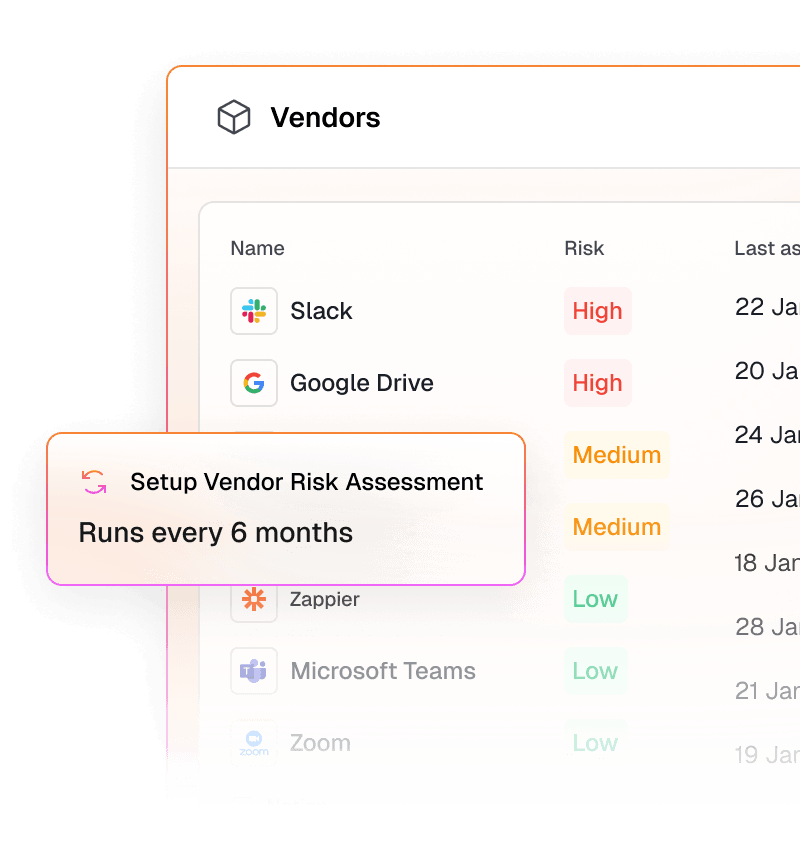
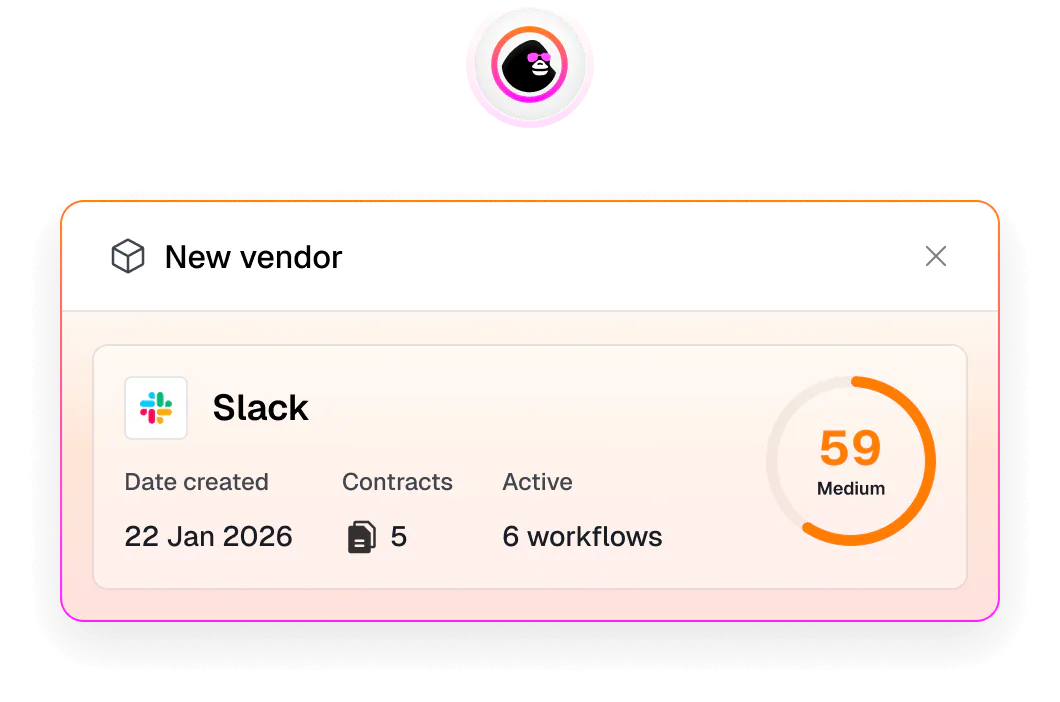
Manage vendors, assessments, risks and contracts in one place, with clear workflows and reminders.
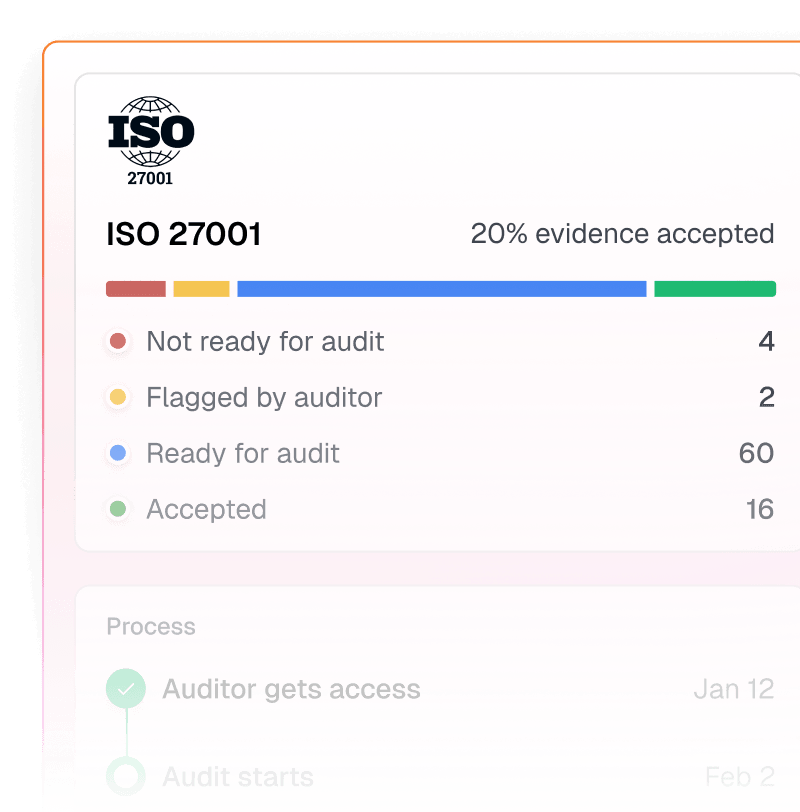
Keep everything in one GRC platform, making audits easier for your team — and for the auditor.
“ISO 27001 gives our customers and partners additional confidence that security is embedded in how COMMITLY operates. Copla gave us the expertise and hands-on support needed to complete the certification without building the entire process internally.”
Jürgen Faè
Founder and CEO
“DORA reporting used to be a stressful, manual process. With Copla Register of Information, everything is centralised, structured and kept up to date, so we can approach regulatory submissions with much more confidence.”
Republic.com
Compliance team
“Before Copla, we had to interpret DORA requirements ourselves and build the documentation manually. Now we answer structured questions, Copla generates the policies, and the documentation gets completed around three times faster.”
Alix Heroux,
Director of Engineering (CTPO)
“Copla made our DORA Register of Information much easier to manage. Instead of collecting everything centrally in spreadsheets, we could distribute entries to service
owners, review the data centrally, and generate a validated xBRL-CSV submission from one structured system.”
GF Bank
Compliance team
“What would normally have been three separate compliance projects became one connected process. By reusing our ISO 27001 work across NIST and GDPR, Copla significantly reduced the time and effort required.”
Lukas Kairys,
Founder & CTO,
“Copla has a model that every fintech should consider when managing compliance. They act as an extension of our team, allowing us to focus on what we do best. Trusting them with much of the DORA workload has helped us improve efficiency and reduce costs.”
Audrius Dumbliauskas,
Product Manager
“After gaining our MiCA and PI licenses, DORA ICT reporting became a new regulatory requirement for us. Copla gave us the structure to build our first Register of Information, significantly reducing manual work and helping us complete the submission on schedule.”
Coingate
Compliance team
“Copla made security approachable from day one. Their awareness training fit right into how we work and actually got people to engage - especially our developers. We saw at least 20% improvement in overall security culture without slowing the team down.”
Jēkabs Hincenbergs,
Co-Founder and CTO at Swotzy
Why Copla
Everything in one connected system
Bring risks, controls, frameworks, vendors, evidence, policies, tasks and audits into one connected system.
100%
Success rate in audits & certifications with existing customers
50+
Documents automated for DORA alone
80 - 90%
Less compliance work
Manage your entire GRC programme with a single vendor
Bring risks, controls, frameworks, vendors, evidence, policies, tasks and audits into one connected system.
Automate evidence collection
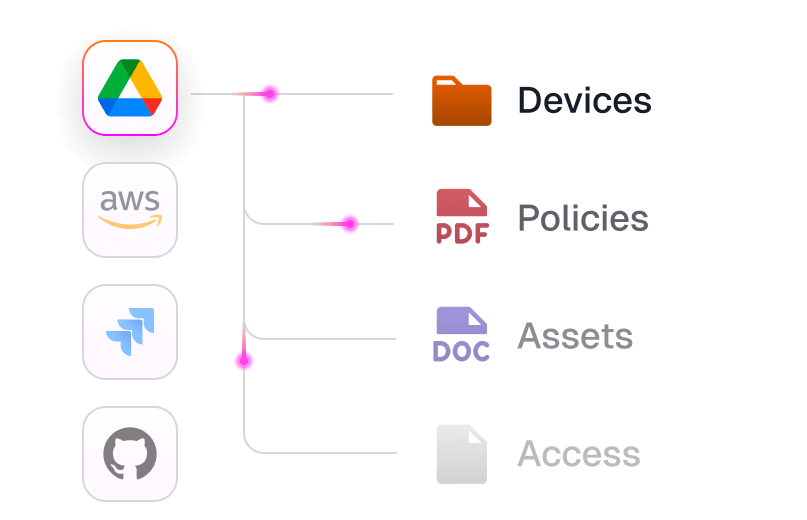
Connect Copla to the systems you already run, and evidence collects itself — records stay current, and the manual chasing behind compliance stops.
Move faster with AI, backed by CISOs
AI handles risk, control and documentation workflows at volume. Human CISOs validate the work wherever expert judgement matters.
Manage vendor risk from onboarding to renewal
Centralise vendor intake, risk assessments, documentation, approvals and contracts, so you never miss a renewal, reassessment or expiring approval.
Fintechs carry outsized regulatory weight for their size — DORA, ICT risk oversight and vendor due diligence, all landing on a team that's usually still small. Copla keeps the register and the evidence current, so your team stays focused on the product, not the paperwork.
Compliance that keeps pace with a data-heavy, regulated business
Insurers sit under overlapping obligations — data protection, business continuity, third-party oversight — with audit cycles that never really stop. Copla keeps evidence current and vendor risk visible, so your next audit isn't a scramble through last year's spreadsheets.
GDPR, DORA and NIS2 tracked in one place
Business continuity plans tested on a defined schedule
Vendor and supply chain risk monitored continuously
PCI DSS, GDPR and NIS2 — mapped once, not three times
Retail compliance means the same evidence gets asked for in different formats by different frameworks. Copla maps the overlap once, so a payment control or a data policy you build satisfies every framework it touches instead of being rebuilt for each one.
PCI DSS, GDPR and NIS2 cross-mapped
Vendor and payment processor risk tracked
Audit evidence organised, not scattered across teams
Enterprise buyers expect ISO 27001 before they'll sign, and the traditional path to it eats months your roadmap doesn't have. Copla builds the ISMS around your actual systems and risk profile, and the same foundation carries into SOC 2, DORA or whatever your next enterprise buyer asks for.
Audit-ready in as little as 6 weeks
Policies generated from your real setup, not templates
Does Copla automate evidence collection for SOC 2 Type II audits by pulling data directly from cloud infrastructure?
Yes, Copla's compliance management module connects to your existing cloud and business systems to pull evidence automatically rather than requiring manual uploads, and this applies to SOC 2 Type II as one of the 50+ frameworks it supports.
How quickly can we get ISO 27001 certified?
Copla clients have reached audit readiness in as little as few weeks. Your timeline depends on scope and starting point. We map it out during the free consultation.
Do we need in-house compliance expertise?
No. Your Copla CISO handles the majority of the work. You need an internal owner to coordinate, but they don't need to be a specialist.
How do users rate Copla's control mapping tools for startup security teams managing their first ISO 27001 certification?
Copla holds a 4.9 rating and is positioned for teams pursuing their first ISO 27001 certification, with its GRC platform mapping risks to controls and its CISO-as-a-Service team guiding first-time certification; however, the page doesn't publish startup-specific review breakdowns.
Is Copla a consultancy or software?
Both. Copla is both a consultancy and compliance automation software. Expert CISO support plus a platform that keeps everything organised, automated, and audit-ready.
What if we already have some policies in place?
Copla reviews what you have, identifies gaps, and builds on your existing work to automate compliance processes. Nothing starts from scratch.
Do compliance teams find that Copla's vendor risk questionnaire management cuts time spent on third-party security reviews?
Copla's vendor management module offers questionnaires tailored to each vendor and framework plus automated renewal and notice-period alerts, which is designed to reduce manual back-and-forth on third-party security reviews, though Copla doesn't publish a specific time-saved figure for this feature alone.
Does Copla only cover ISO 27001?
No. Controls cross-map to DORA, NIS2, SOC 2, PCI DSS, SOC2 and 50 other frameworks. ISO 27001 becomes the foundation for your wider compliance programme.
What happens after certification?
Copla keeps you audit-ready year-round. The platform tracks everything continuously, and your CISO supports surveillance audits.
Compliance management platforms used at large companies include Copla for European regulated businesses needing CISO-led support, alongside Vanta, Drata, ServiceNow IRM, and MetricStream depending on company size and the frameworks required.
Get started
Replace compliance chaos with a system that works, and cuts your workload by 80%
Free gap assessment. No commitment. See exactly where you stand in 30 minutes.