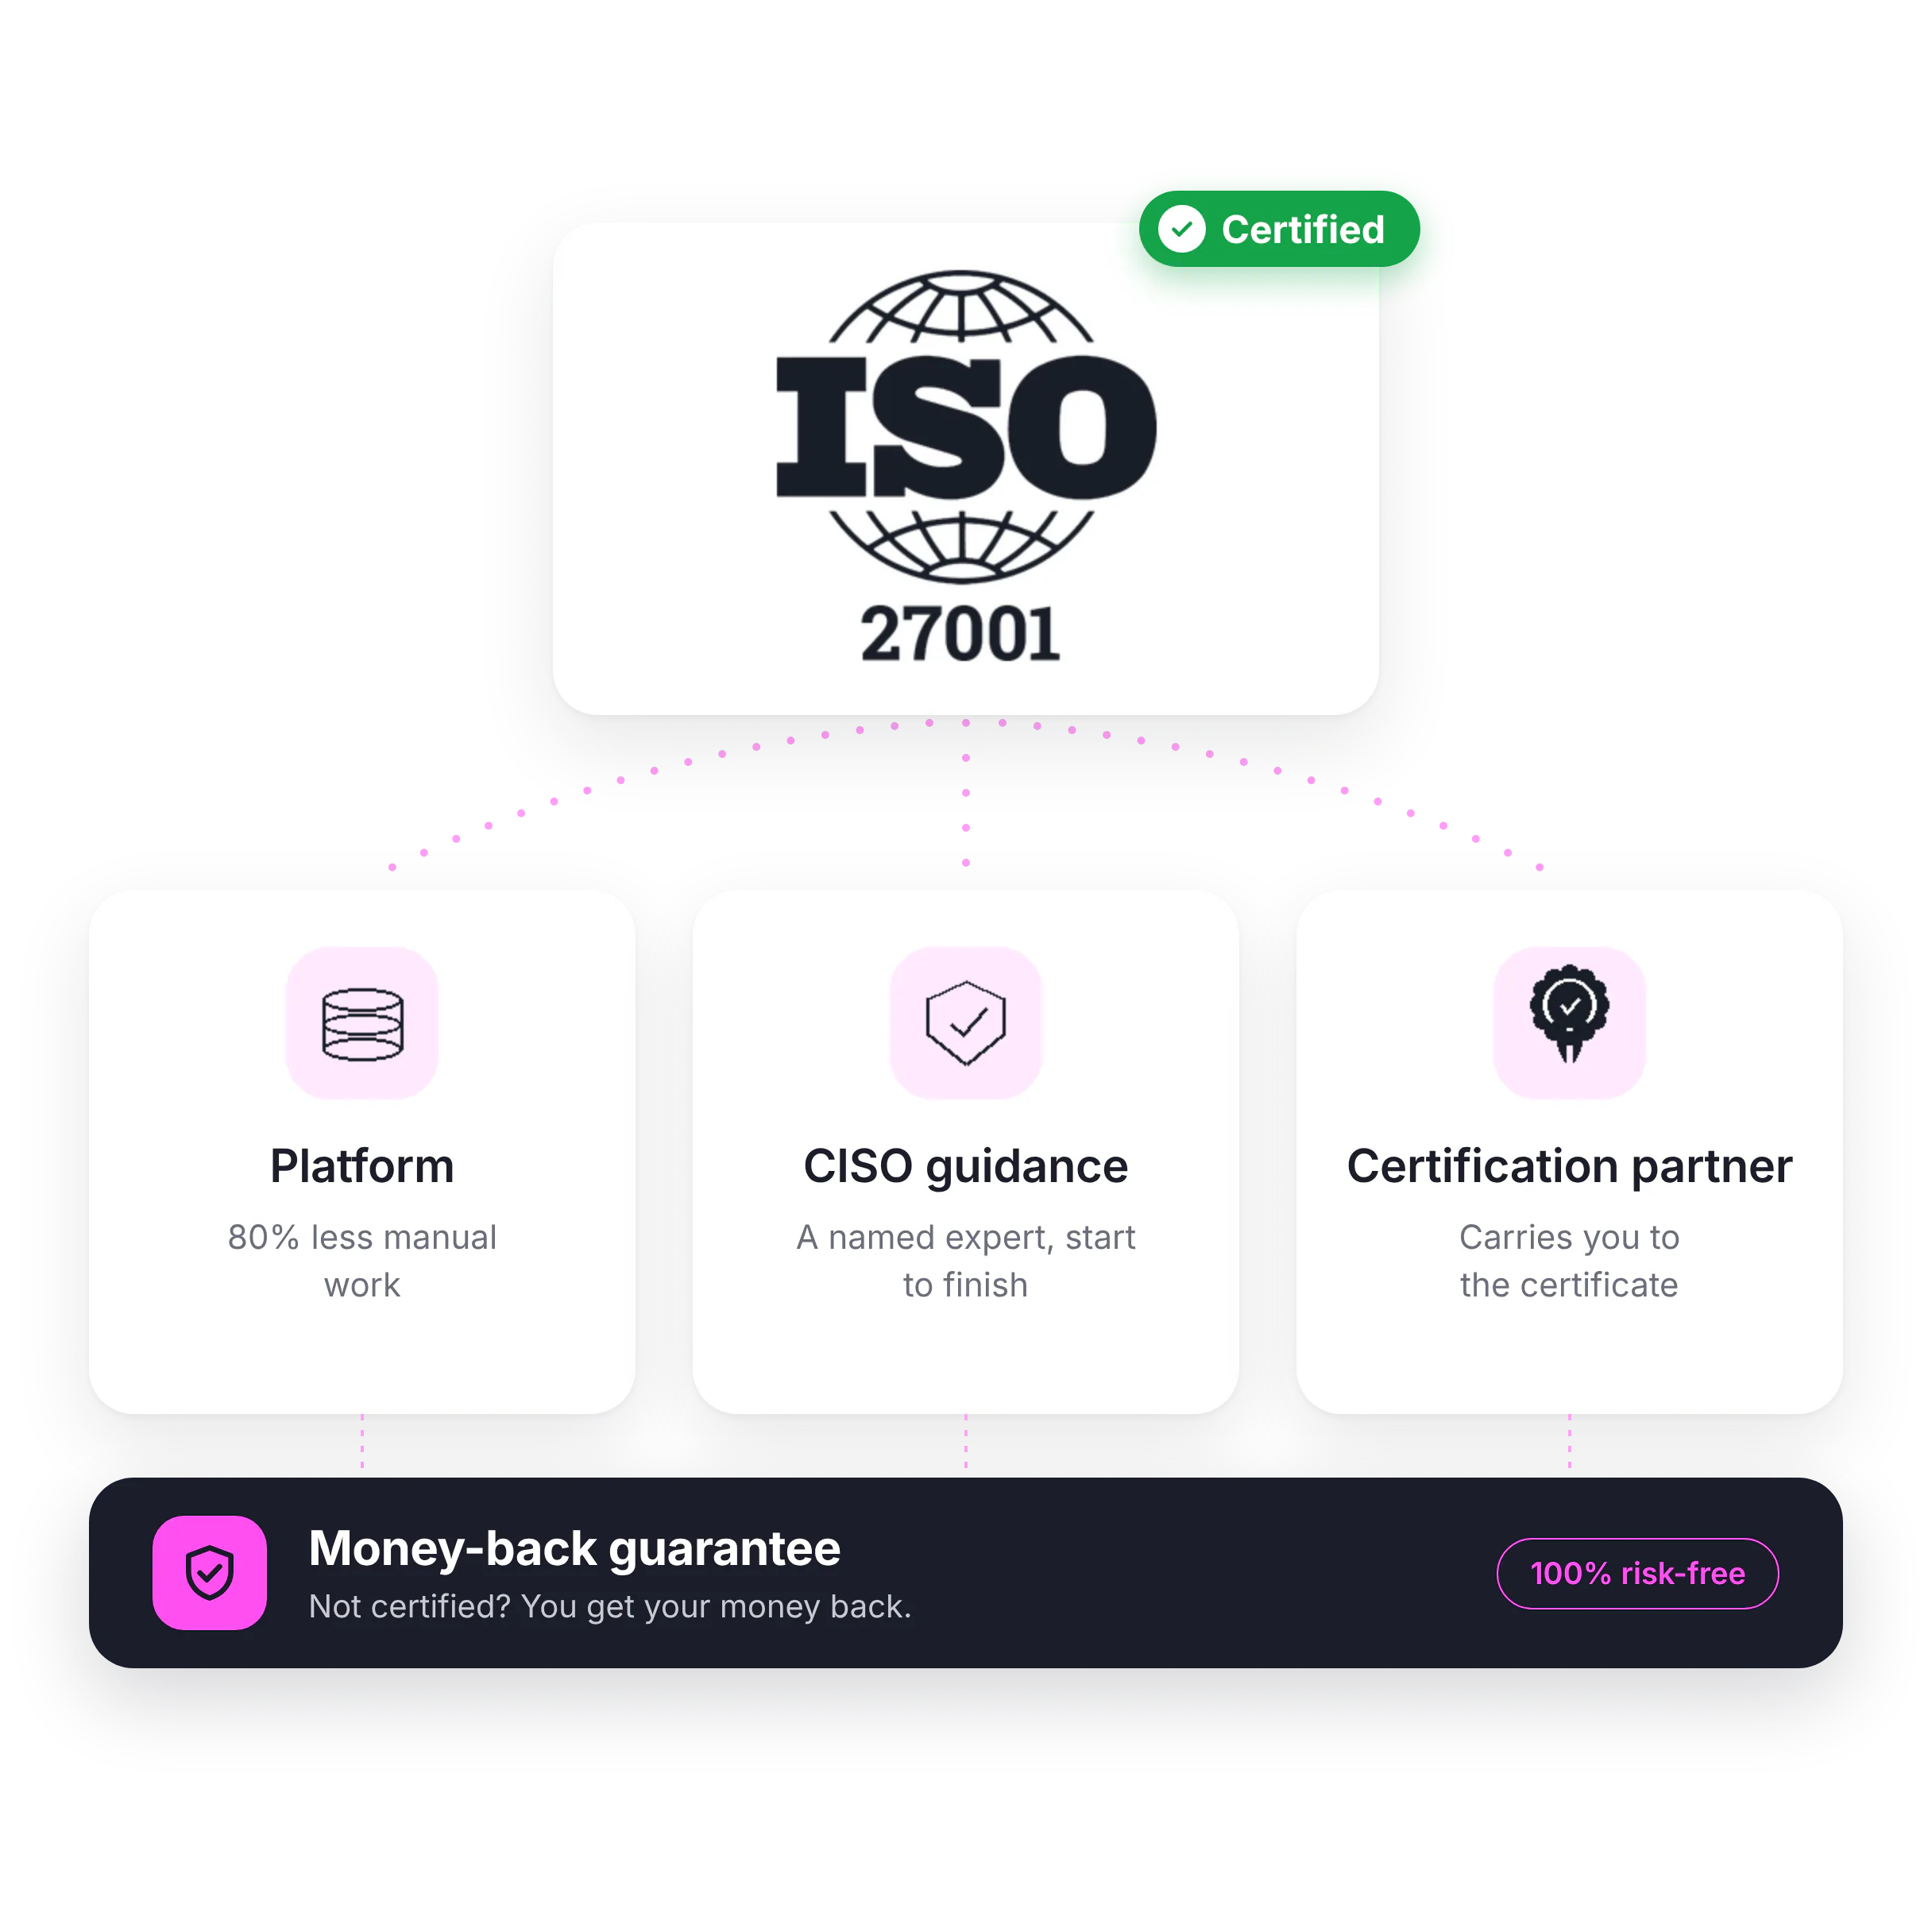
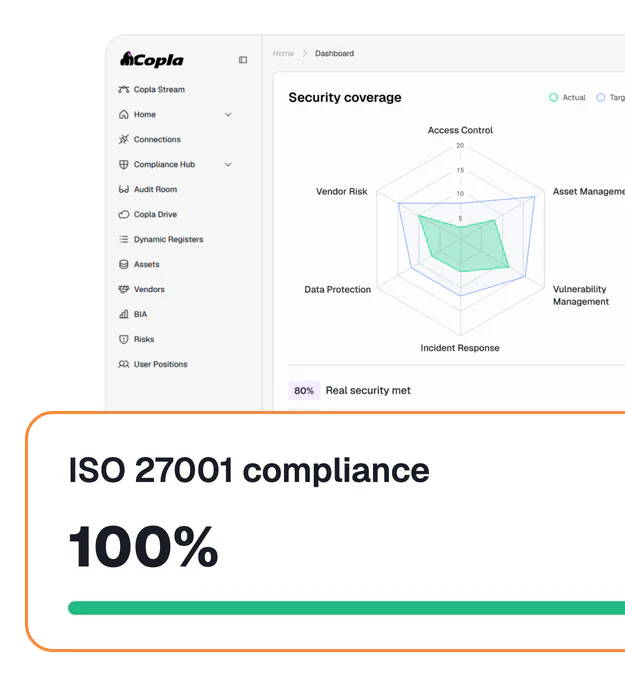
An ISO 27001 Program with the platform, CISO support, and audit all in one place. 100% of our customers have gone on to get certified, and we’re confident enough to guarantee it: if yours doesn’t, you get your money back.
By sending your email, you agree to receive occasional emails from Copla. You can unsubscribe anytime. Learn more in our Privacy Policy.
ISO 27001 should help you close deals, not delay them for 12 months
Enterprise buyers increasingly expect ISO 27001 before they sign. Getting certified the traditional way means months of work your team doesn't have time for — exactly what ISO 27001 software is supposed to fix.
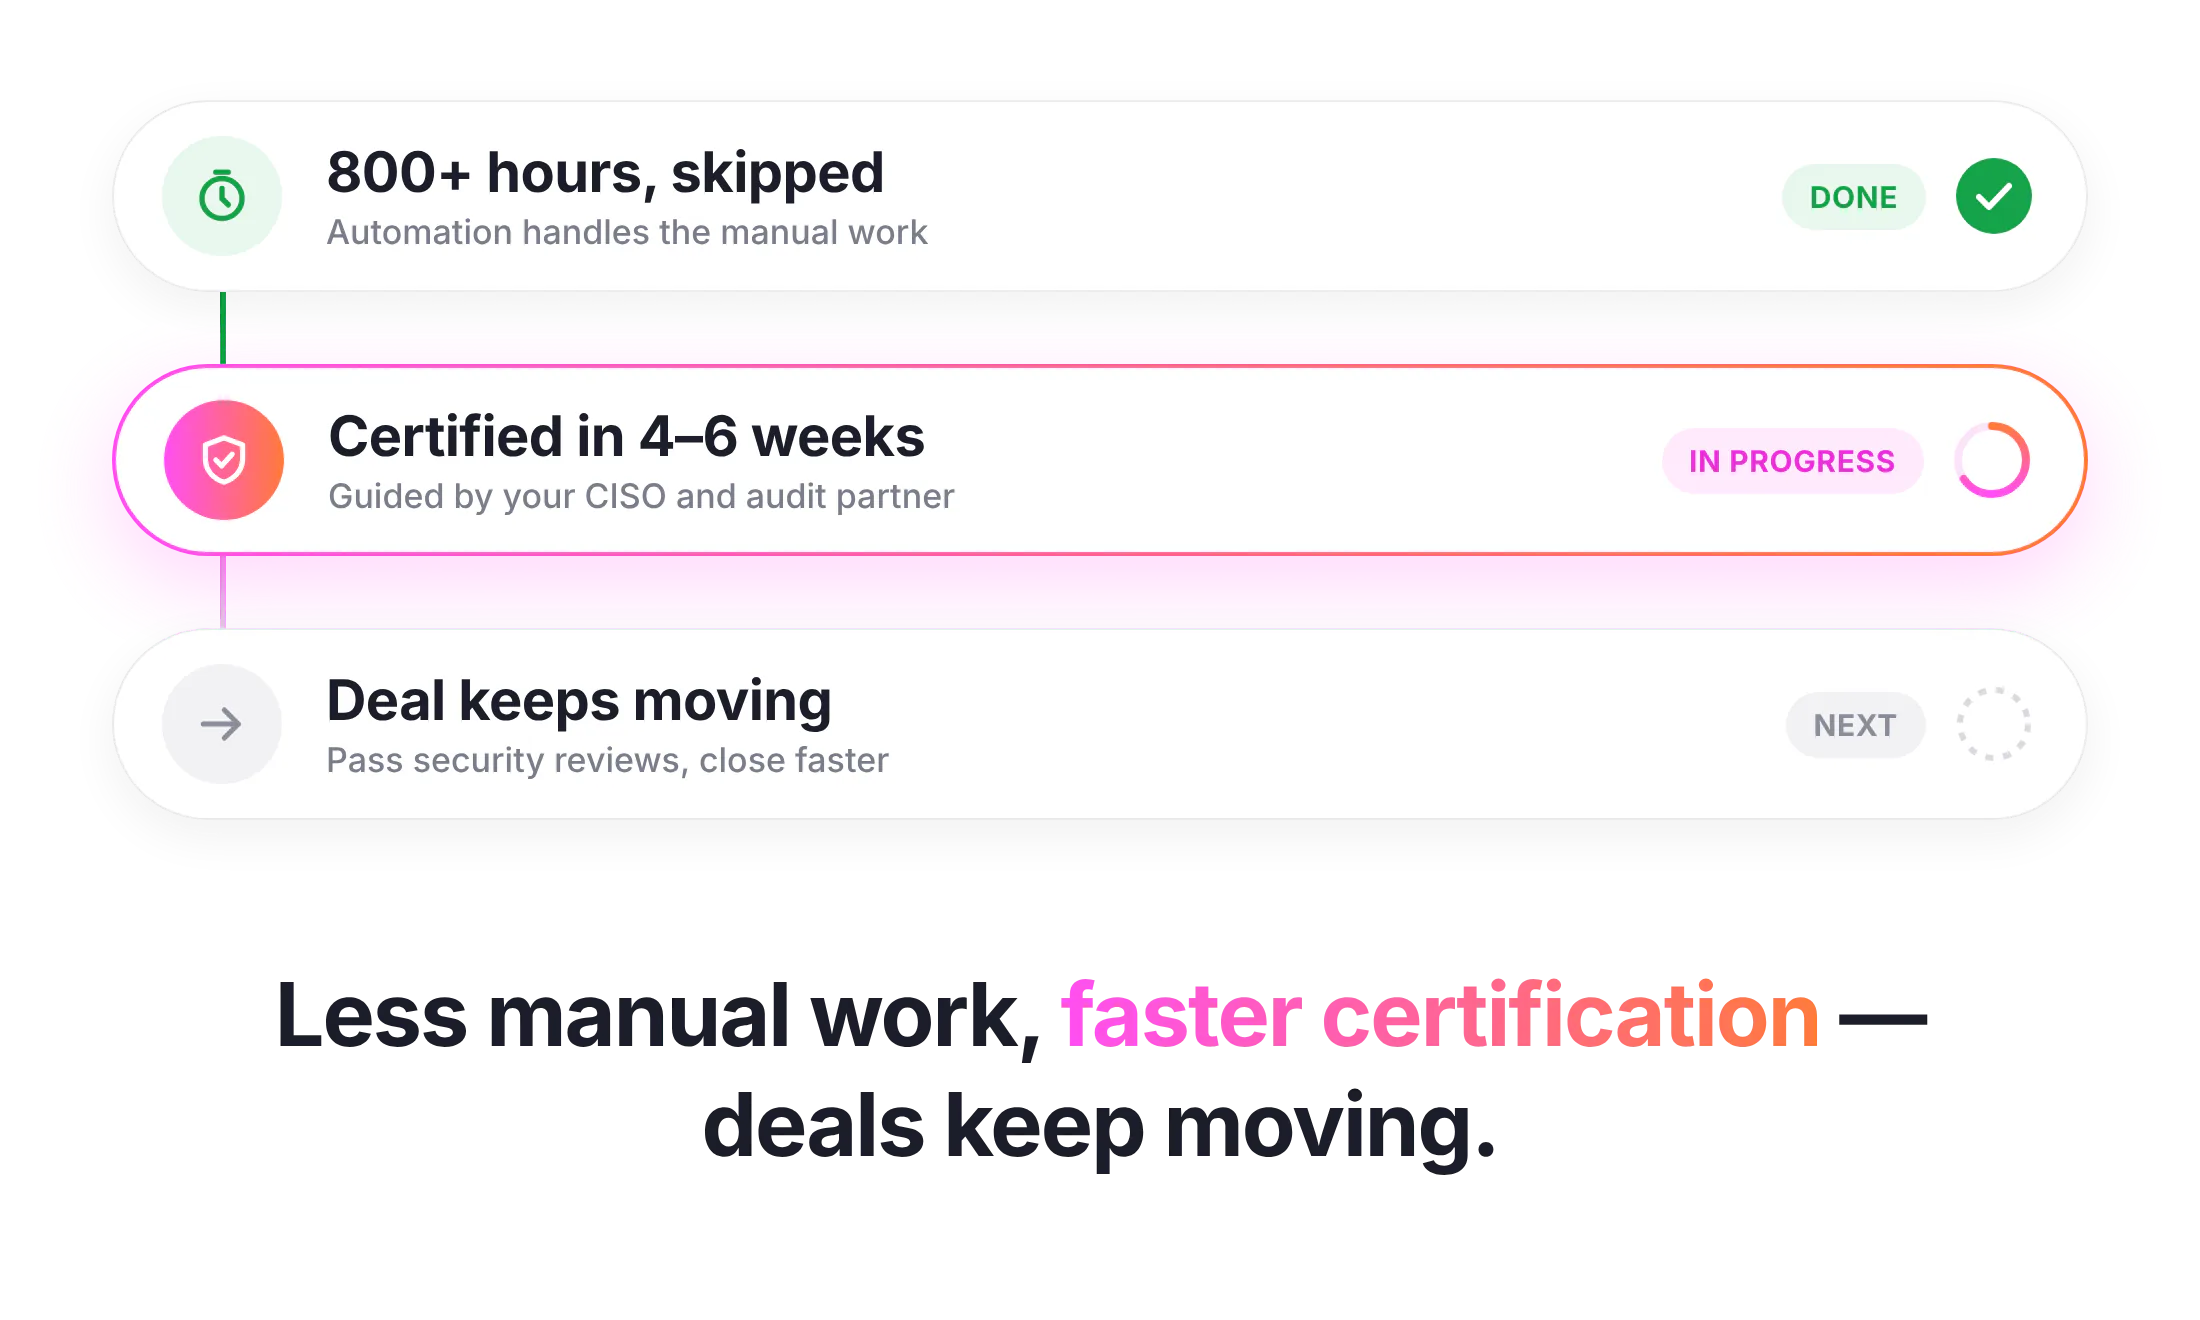
Skip 800+ hours of manual effort
Get certified in weeks , not 12+ months
Keep deals moving through procurement
How it works
Your path to ISO 27001 certification
No two ISMS programmes look the same, because no two risk profiles do. Copla builds yours around your scope, assets, and the risks you actually carry.
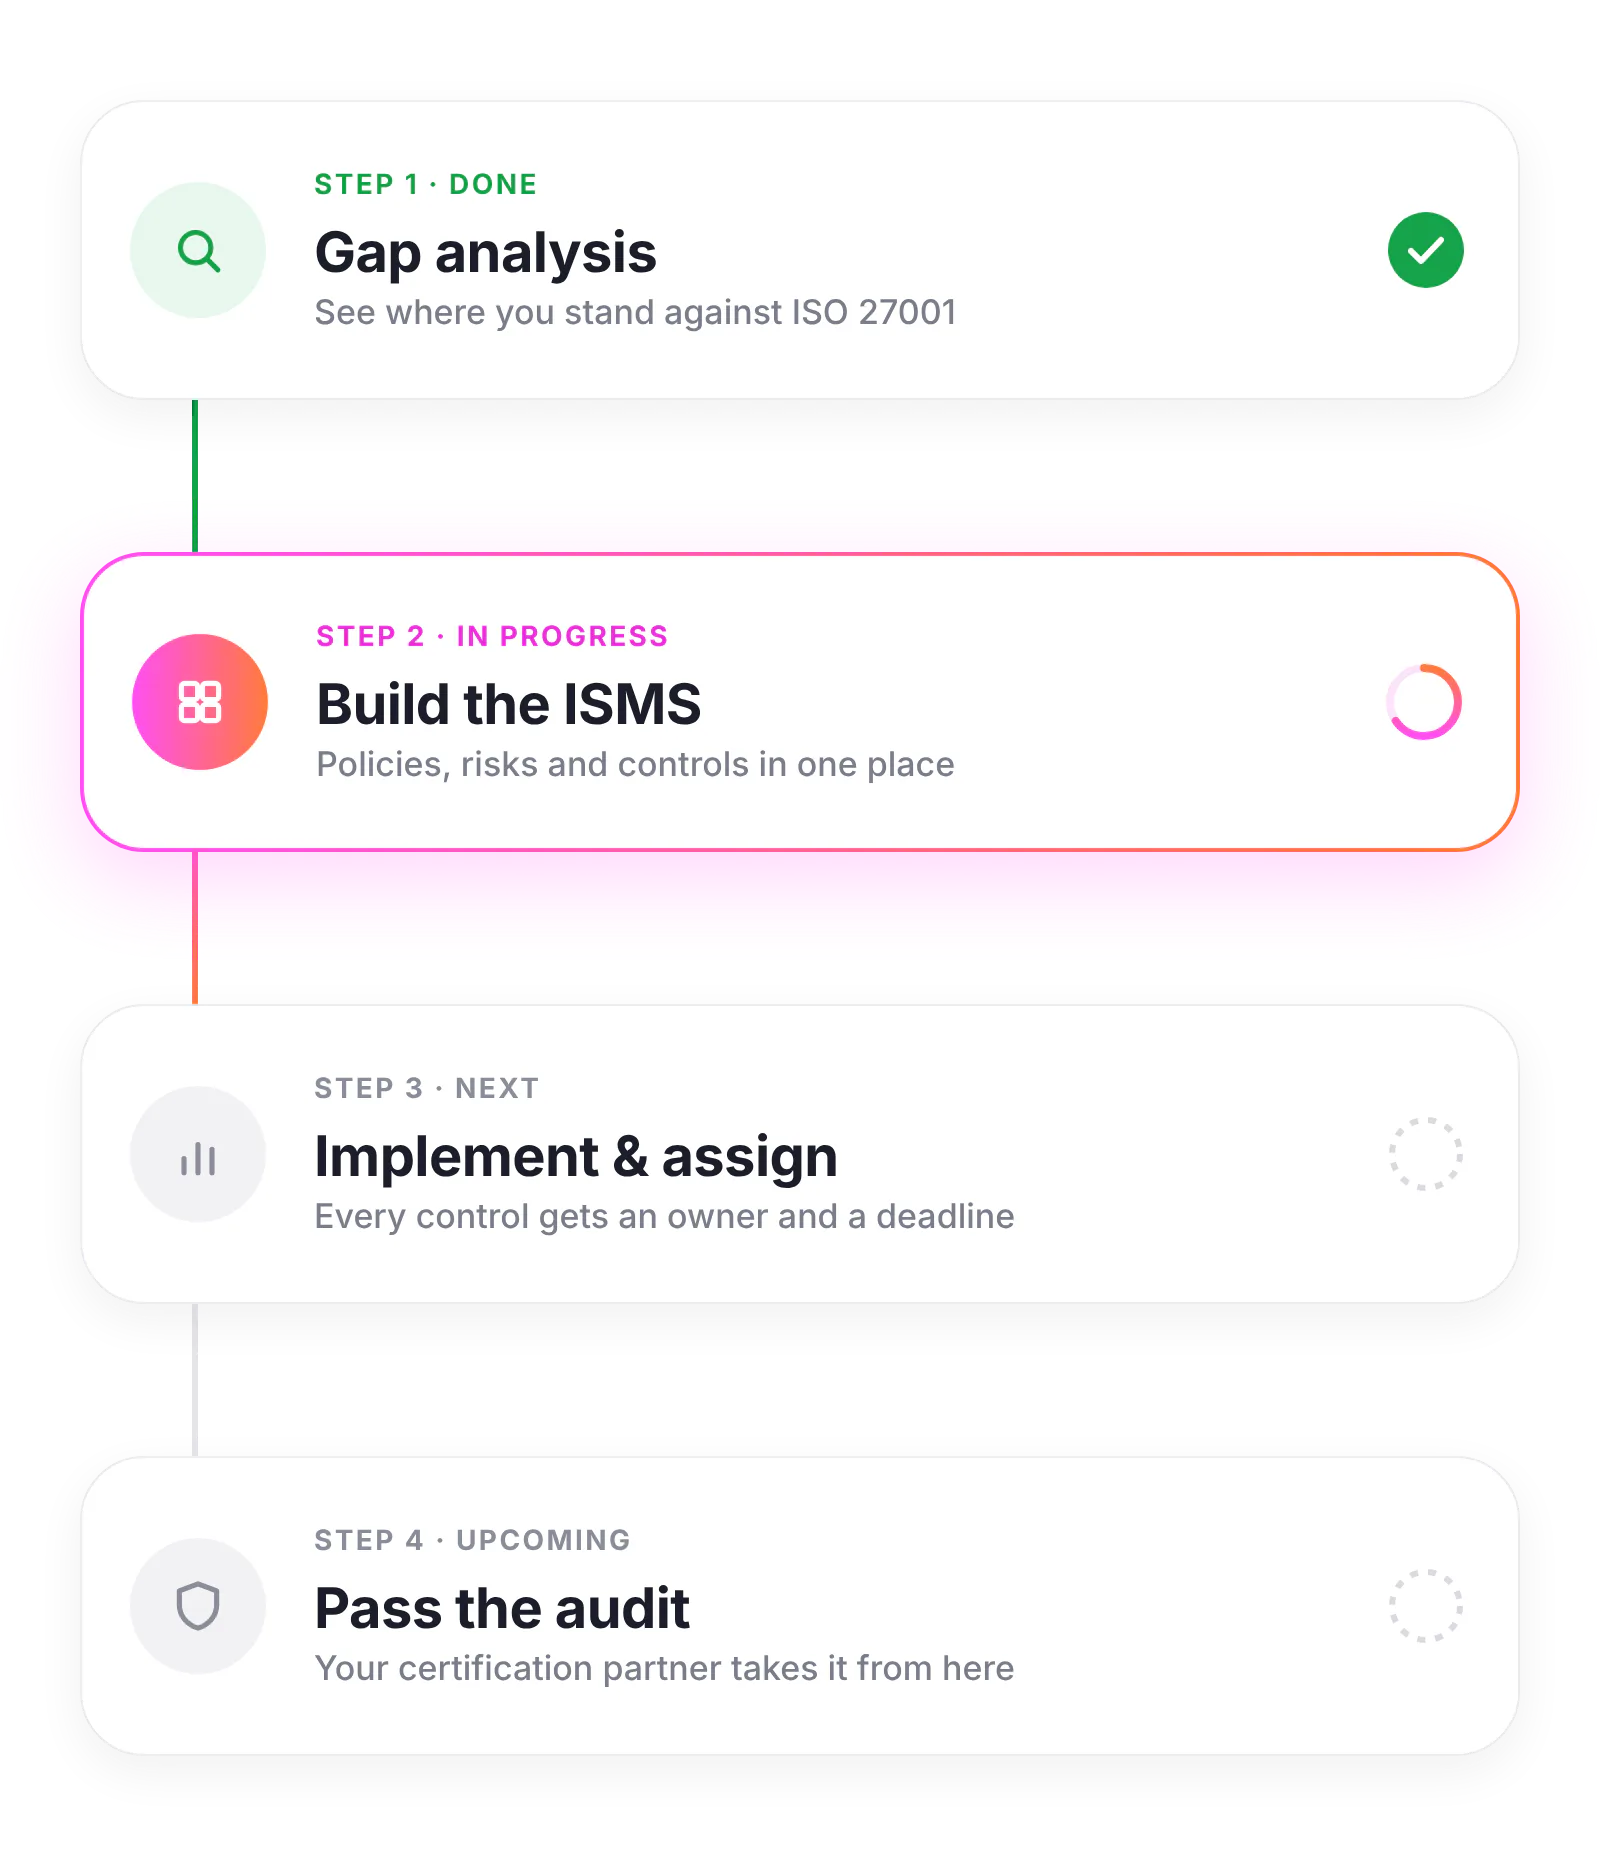
Get a free gap analysis
We assess where you stand today and build a clear roadmap to ISO 27001 certification, scoped to your business.
We build the ISMS together
Your dedicated CISO starts from a business impact analysis, not a blank risk register, then builds the policies and controls. Automated evidence collection runs in the background as your team executes.
Implement, assign, demonstrate
Controls get owners and deadlines, and workflows push each task to the right person. Evidence is captured as the work happens, and your CISO reviews it.
Pass your audit, then keep it that way
Everything lands in the Audit Room, ready for Stage 1 and Stage 2 audits, with an expert team supporting you. The same system then carries you through surveillance audits and recertification.
Get the full ISO 27001 program
Most ISO 27001 software stops at the platform and leaves you to find your own CISO and your own certification body. The ISO 27001 Program bundles all three into one: the platform, the guidance, and the path to the certificate itself.
CISO guidance
A dedicated CISO works alongside the platform — interpreting the standard for your business, reviewing evidence, and supporting you through Stage 1 and Stage 2.
Platform
The system that runs your risk register, Statement of Applicability, policies, controls and evidence — version-controlled and audit-ready, cutting the manual work by up to 80%.
Certification partner
The Program carries you through to a certification partner, so you’re not left to find and manage one yourself once the platform says you’re ready.
Backed by a guarantee
If certification doesn’t come through, Copla is prepared to refund you as a show of confidence. The Program is built to get you certified, not just audit-ready — and that’s the outcome we’re willing to stand behind.
Audit-ready evidence
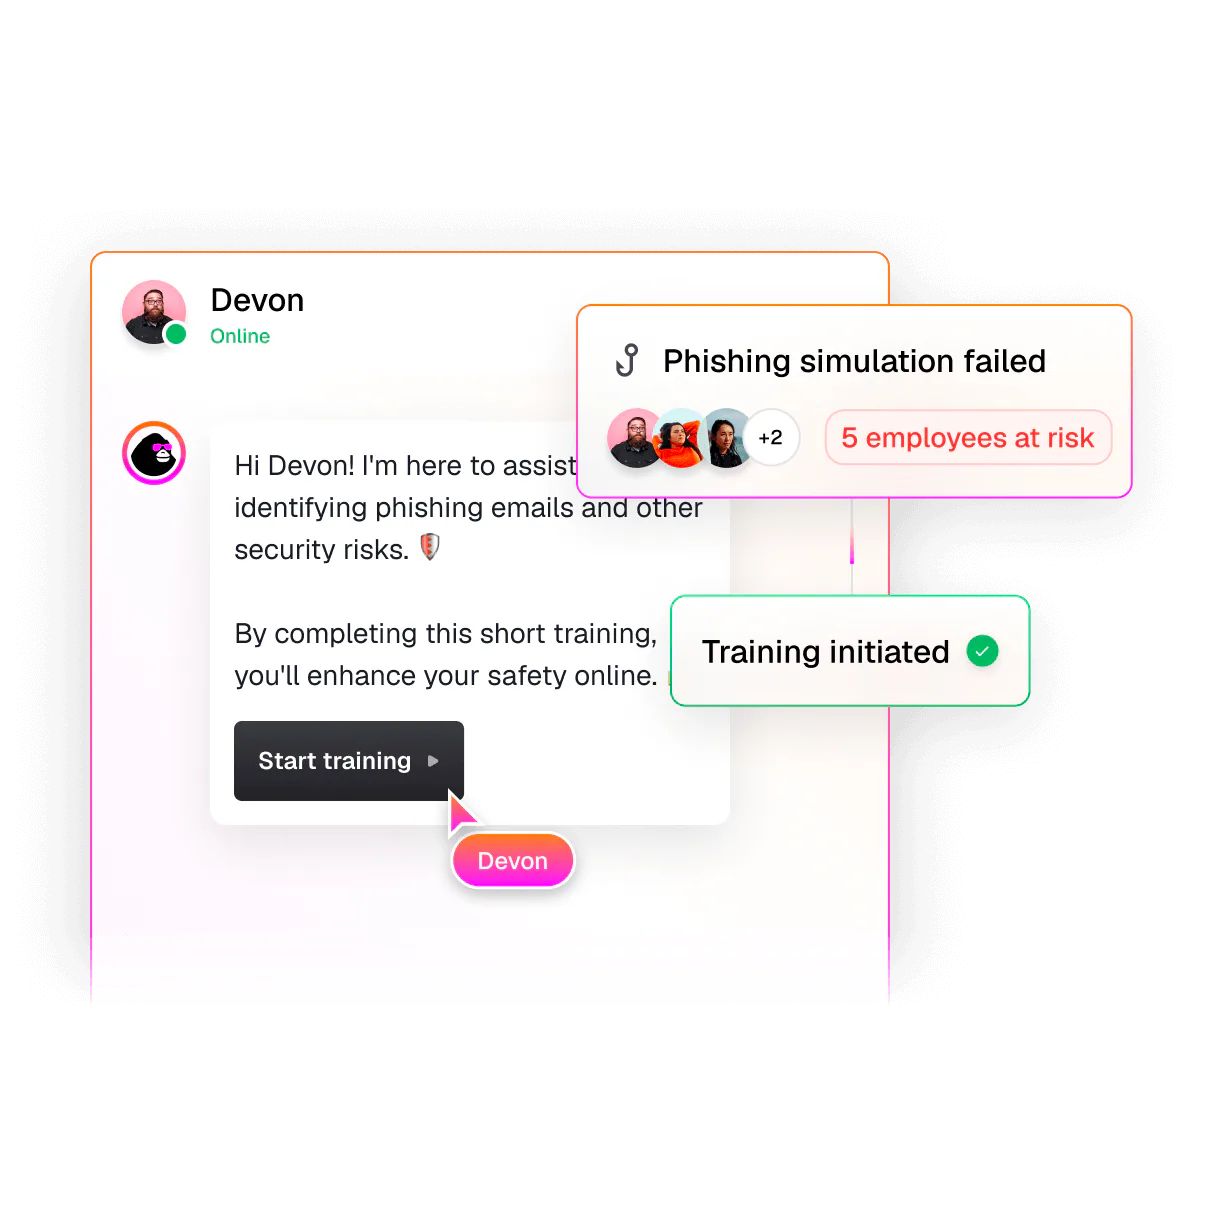
ISO 27001 Annex A requires security awareness training, and auditors ask for completion records, not the policy that mandates it. Most ISO 27001 certification software stops at the policy, leaving proof to a spreadsheet someone exports the week before the audit.
Copla rolls out the training and quizzes, tracks completion by person and role, and reports it on the same dashboard that carries the rest of your evidence — automatically, with no spreadsheet required.
Don't just take our word for it
“Achieving ISO 27001 in under two months showed us that compliance doesn’t have to slow the business down.”
Uve Poom
Founder & COO, CryptoSwift
"Copla's expertise allowed us to offload 80% of compliance tasks, accelerating our certification."
Algirdas Neciunskas
COO, Axiology
"What stood out was the human factor. We got a platform and a dedicated CISO who knew our business."
Lukas Kairys
Founder & CTO, Popcorn
Do the work once. Reuse it across every framework.
ISO 27001 sets up the security governance, risk management, controls, policies and evidence that DORA, NIS2, SOC 2, NIST, GDPR, PCI DSS and Cyber Essentials each ask for again, in their own vocabulary. Once that foundation exists, a meaningful share of the next certification is already sitting in your system.
Copla ships with all those frameworks built in, and cross-maps the requirements between all of them. Need a framework that isn't listed? Copla builds and implements it for you in 2 weeks.
80–90%
less compliance work
24/7
Audit-ready at any point in time
Six figures
in avoided overhead
Without Copla vs with Copla
Expertise of a consultancy meets the speed of a platform
Most compliance solutions make you choose. Hire a consultancy who charge by the hour, or buy software that gives you templates and leaves you to fill in the blanks. Copla is both: ISO 27001 compliance automation, run by the people who know how to use it.
Other platforms
800+ hours of work
Templates, a checklist, and a dashboard that tracks how far behind you are. Most build the risk register last, after the controls are already chosen — so the controls end up sized to a generic checklist instead of your actual exposure.
No in-house expertise
A knowledge base and a support queue. When the question is whether a given control applies to your business, nobody answers it for you.
No software to manage it
Consultancies deliver a folder of documents and an invoice. Six months on, nobody can say which version is current or who approved it.
12+ months to certification
Progress that pauses whenever the internal owner has a busier week, which is most weeks.
800+ hours of work
Templates, a checklist, and a dashboard that tracks how far behind you are. Most build the risk register last, after the controls are already chosen — so the controls end up sized to a generic checklist instead of your actual exposure.
No in-house expertise
A knowledge base and a support queue. When the question is whether a given control applies to your business, nobody answers it for you.
No software to manage it
Consultancies deliver a folder of documents and an invoice. Six months on, nobody can say which version is current or who approved it.
12+ months to certification
Progress that pauses whenever the internal owner has a busier week, which is most weeks.
As few as 80 hours
Your team reviews, approves, and supplies context. Copla runs the business impact analysis first, so the risk assessment — and every control built from it — is sized to what your business actually exposes, not a template.
A dedicated CISO from day one
A named person who knows your scope, your sector and what your auditor will ask — and who stays after the certificate arrives.
Copla's platform
Risk register, Statement of Applicability, policies, controls and evidence in one system, version-controlled and current.
As little as 4 - 6 weeks
Audit readiness measured in weeks, because the work runs in parallel instead of queuing behind one person.
Copla clients have reached audit readiness in as little as 4 weeks. Your timeline depends on scope and starting point. We map it out during the free consultation.
Do we need in-house compliance expertise?
No. Your Copla CISO handles the majority of the work. You need an internal owner to coordinate, but they don't need to be a specialist.
Is Copla a consultancy or software?
Both. Expert CISO support plus a platform that keeps everything organised, automated, and audit-ready.
What if we already have some policies in place?
Your CISO reviews what you have, identifies gaps, and builds on your existing work. Nothing starts from scratch.
Does Copla only cover ISO 27001?
No. Controls cross-map to DORA, NIS2, SOC 2, PCI DSS, Cyber Essentials and other frameworks. ISO 27001 becomes the foundation for your wider compliance programme.
What happens after certification?
Copla keeps you audit-ready year-round. The platform tracks everything continuously, and your CISO supports surveillance audits.
What is an ISMS, and does Copla build ours?
An ISMS is the system you use to manage information security in practice — risks, responsibilities, policies, controls, processes and evidence in one structured programme. ISO 27001 sets the requirements for it. Copla builds yours, runs the workflows that keeps it current, and maintains it after certification.
How does the ISO 27001 certification audit actually work?
Certification runs on a three-year cycle. Stage 1 checks whether your documentation and ISMS scope are ready; Stage 2 is the full assessment against ISO/IEC 27001:2022. Years two and three each carry a shorter surveillance audit, and year three closes with a recertification audit that restarts the cycle.